I maintain AEGIS at Escape Studio; AI assisted development and this post. AEGIS is a free, MIT-licensed Windows-first security beta for local AI agents.
A skill is a set of instructions that can include shell commands and permission changes. The review question is practical: does this instruction ask the agent to skip a confirmation step, and where is that request in the file?
AEGIS can review a selected local skill, project or supported agent profile and show findings with their source context. The screenshot below illustrates an approval-bypass instruction in a simulated review fixture. That gives the operator a concrete passage to inspect before deciding whether to use the skill.
The next protection step is explicit configuration. A command routed through AEGIS’s execution policy can be denied before launch. On the configured Model Context Protocol gateway, a one-use approval matches the exact tool and arguments; changed arguments need a matching new grant. Process pause and stop are manual, with an identity check.
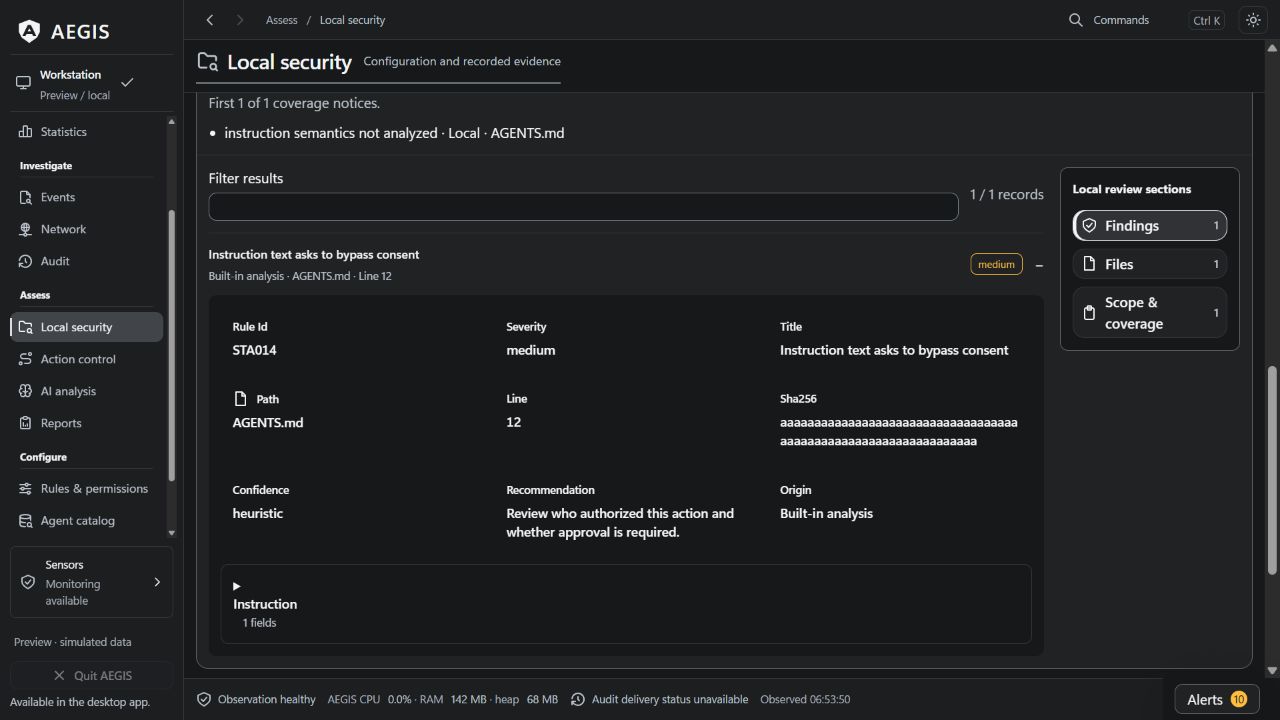
Captured 27 October 2026 from the current source UI preview; simulated data, no live blocking test.
Public beta: 0.20.1-beta. Windows is the primary platform; macOS/Linux are experimental. The enforcement controls cover configured routes.
Source, beta and contribution guide: GitHub - antropos17/Aegis: Windows-first desktop oversight for AI agents: live monitoring, local security reviews, token usage, audit reports and opt-in action policies/MCP gateways. Experimental Hyper-V guest execution; macOS/Linux experimental. · GitHub
When reviewing a skill, what source context would help you decide whether its command is appropriate for your project?